Workforce identity fraud is creating challenges across recruitment, onboarding and cybersecurity, yet organisations remain divided over which team should take responsibility for preventing it.
A report from Entrust, based on a survey of 1,000 IT and security leaders, found that only 8% believed the chief human resources officer (CHRO) or HR team should have primary responsibility for workforce identity security. Meanwhile, 45% assigned primary ownership to the chief information security officer (CISO) or security team, 22% to IT and 20% to the chief information officer (CIO).
Just 4% supported genuinely shared ownership, highlighting a potential accountability gap in how organisations manage identity risks.
For HR leaders, the findings raise an important question: how can organisations prevent fraudulent candidates and impersonation attempts if identity checks are not clearly managed across recruitment, onboarding and IT security?
Identity Risks Can Begin Before Hiring Is Complete
Workforce identity security extends beyond protecting employee accounts and login credentials. Risks can emerge during recruitment, when employers assess whether candidates are who they claim to be.
In the Entrust survey, more than a quarter of respondents said they had experienced or investigated candidate fraud in the previous 12 to 24 months. Another 30% reported concerns about identity fraud involving new hires.
Confidence in verification also remained limited. Only 39% of respondents said they were confident in their ability to verify an individual's identity during hiring, rising to 43% during onboarding.
These gaps can create problems if an organisation relies on informal checks or assumes that another department is responsible for confirming a person's identity.
The risks do not end once an employee joins. Identity can also be compromised during account recovery, remote access, changes in job responsibilities and offboarding. Each stage requires appropriate controls and clear responsibility.
AI Is Making Identity Verification More Challenging
Advances in generative AI are adding complexity to existing verification processes. Fraudulent applications can involve manipulated documents, synthetic identities, deepfake video and cloned voices.
These techniques can make it harder for recruiters and support teams to rely solely on visual checks, interviews or information supplied by an applicant.
For HR, this does not mean every unusual application is fraudulent. It does mean that organisations may need consistent verification procedures, additional checks where appropriate and clear escalation routes when something does not add up.
Verification should also be proportionate to the role and risk involved. Applying intrusive checks indiscriminately can create unnecessary friction for genuine candidates and raise privacy concerns.
Why HR and IT Need Clear Ownership
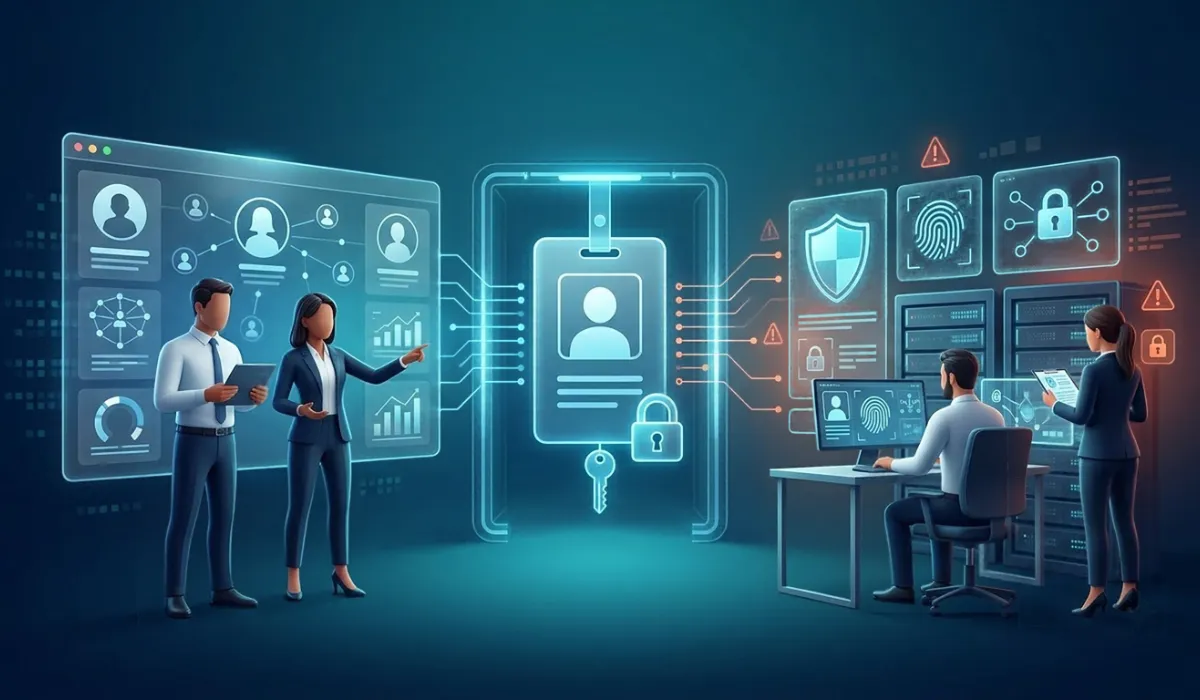
HR typically manages recruitment and onboarding, while IT and security teams control identity systems, access permissions and technical safeguards. Both have a role in reducing workforce identity risks, but responsibilities can fall through the gaps when their processes are not aligned.
A practical approach is to define ownership at each stage of the employee lifecycle.
HR and talent acquisition teams can establish when identity verification is required, what triggers additional review and how candidates are informed about the process. IT and security teams can determine appropriate verification controls, access requirements and escalation procedures.
Legal, privacy and compliance specialists should also be involved where checks involve sensitive personal information or different national requirements.
Organisations should document who makes decisions, who investigates exceptions and who can approve a candidate or employee when verification cannot be completed through the standard process.
Practical Steps HR Can Take
HR teams do not need to manage cybersecurity independently to help close identity gaps. They can work with specialist teams to improve how risks are identified and handled.
- Define verification requirements. Establish which roles require identity checks, when those checks should occur and what circumstances warrant additional review.
- Agree on escalation procedures. Give recruiters and onboarding teams a clear process for handling inconsistent documents, failed checks or suspected impersonation without relying on informal judgement alone.
- Integrate HR and security workflows. Where practical, connect identity verification processes with existing HR systems and security controls to reduce duplicated work and inconsistent records.
- Consider international candidates. Ensure verification processes can accommodate legitimate identity documents from different countries, including varied languages and character sets, while meeting applicable privacy and legal requirements.
- Review the process regularly. Track suspected fraud, verification failures, delays and exceptions. Use these findings to improve procedures without treating every discrepancy as evidence of wrongdoing.
Building Accountability Across the Employee Lifecycle
Workforce identity security is not simply an IT issue or an HR responsibility. It involves decisions that begin during recruitment and continue through onboarding, employment and departure.
The Entrust findings suggest that organisations need greater clarity about who owns each part of the process. For HR leaders, the priority is to establish that accountability with IT and security teams before a verification issue becomes a wider operational problem.
Clear responsibilities, proportionate identity checks and coordinated workflows can help organisations protect their workforce while maintaining a fair and practical candidate experience.
Research source: Entrust - Know Your Employee: Workforce Identity Report